Tuesday, May 19, 2020

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

Well, Windows users have a bad habit of removing files from recycle bin. Deleting useless files from Recycle Bin helps a user to save some storage space which can improve the speed of a computer. However, Windows users do that more frequently and later regret. Actually, Recycle Bin is a place from where we can get back our deleted files and folders.
Sometimes, we accidentally delete our important files and folders and due to some reason we lose them from Recycle bin too! At that time, we search for recovery methods. Well, there are many methods available over the web which can help you to recover deleted files from computer, but, when it comes to reliability, nothing can beat EaseUS.

What Is EaseUS Data Recovery Wizard?

EaseUS is one of the leading software providers which is known for its data recovery programme. EaseUS offers some free data recovery software that can help you to recover deleted, formatted or lost data from PC, laptop or removable device easily and quickly.
One of the best thing about EaseUS is that it provides tools for recycle bin recovery which can help you to get back files that you have deleted from the Recycle bin itself. EaseUS Data Recovery Wizard free can easily recover lost files, pictures, documents, videos and more from deleting, formatting, partition loss, OS crash, virus attack and other data loss cases.

How To Recover Deleted Files?

If you are struggling to get back your lost data files, then here is an easy data recovery method which will help you to get back deleted files on your computer. Below, we are going to share a mini guide on how to use EaseUS Recycle Bin Recovery to get back your deleted data.
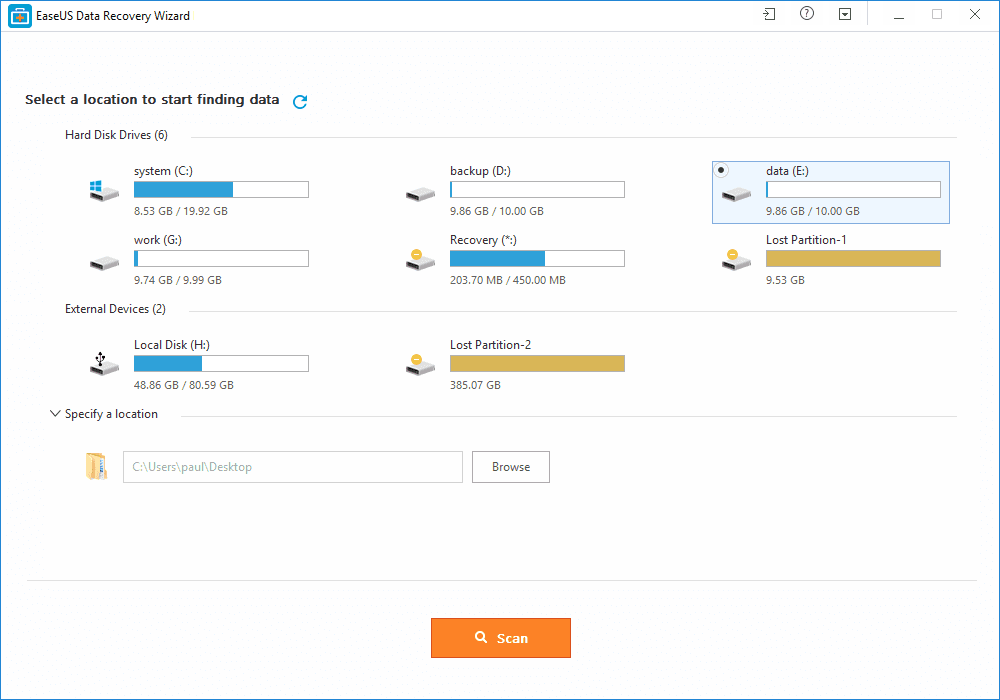
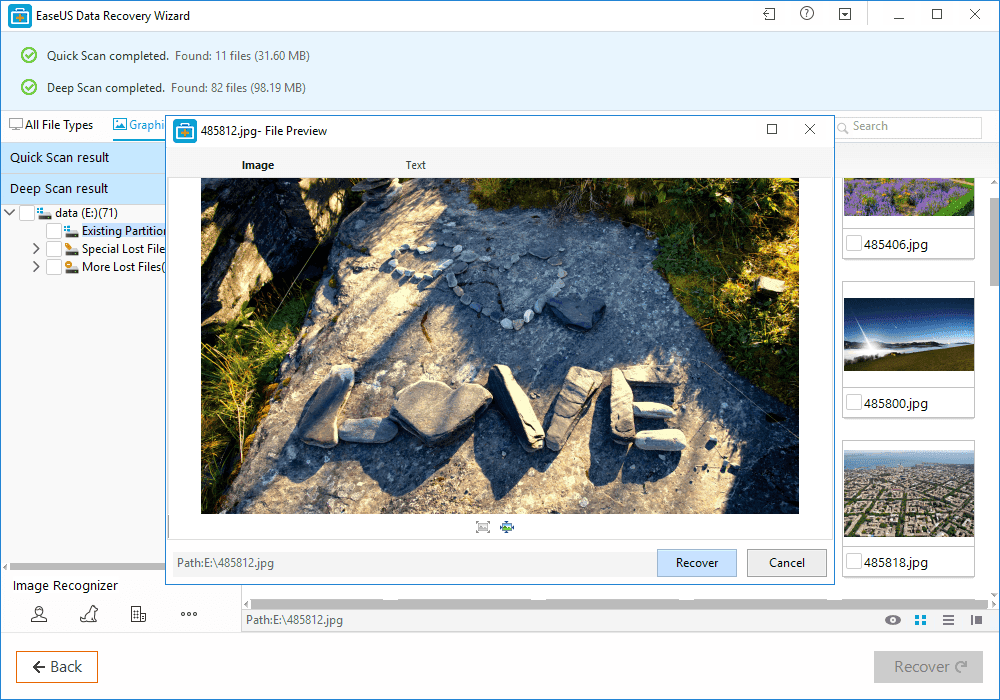
Step 1. First of all, you need to download and install EaseUS Data Recovery Wizard on your Windows computer and then launch it normally. You need to select the location where you want to scan and then click on 'Scan'
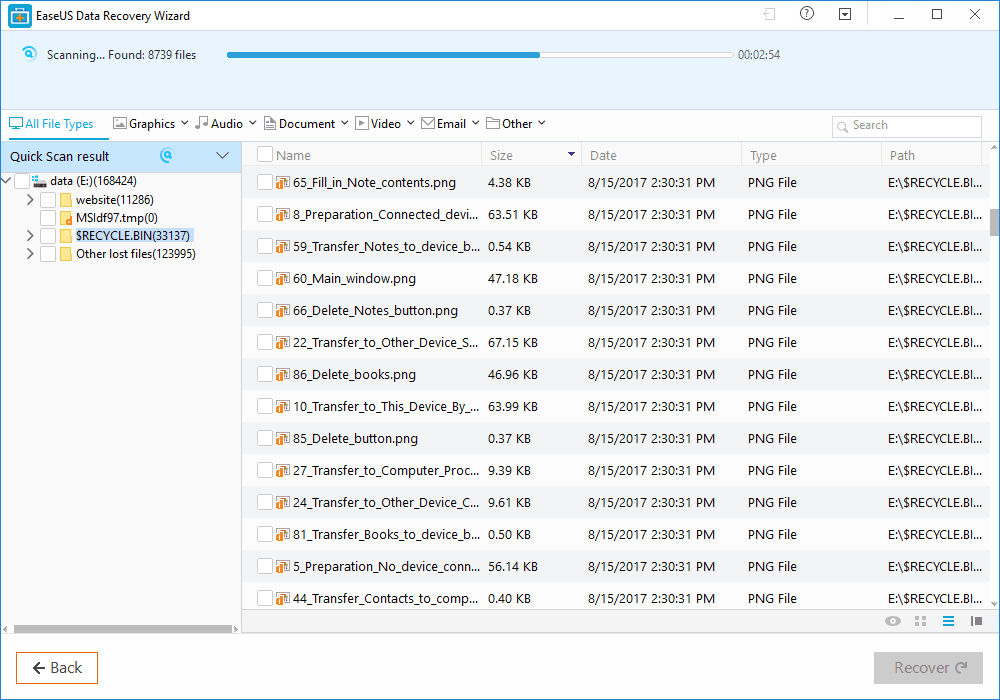
Step 2. Now, wait for few minutes until the tool finishes scanning your drive. The tool search for files that got deleted or cleaned from the Recycle Bin.
Step 3. Now it will show you files that you can recover. Here you need to click on the file which you want to recover and click on 'Recover'
That's it, you are done! This is how you can use EaseUS data recovery to get back your deleted files on your computer.

Benefits of EaseUS Data Recovery

Well, the data recovery tool provided by EaseUS comes with many benefits. It can not only recover accidentally deleted files, but it can also recover data in case of Virus Attacks, Hard Disk Damage, OS Crash etc.
You can also use this awesome data recovery wizard to recover deleted files from External Disk, USB Drive, Camcorder, Mobile Devices, Zip Drive, iPod, Music Player and more.
Overall, this is one of the best data recovery tools you can have on your Windows computer. EaseUS Data Recovery also has a free version with restricted features. Overall, this is a stress-free solution to get back your deleted files
Related news

Monday, May 18, 2020

5 BEST HACKING BOOKS 2018

Most of the people don't go with videos and read books for learning. Book reading is a really effective way to learn and understand how things work. There are plenty of books about computers, security, penetration testing and hacking. Every book shows a different angle how things work and how to make system secure and how it can be penetrated by hackers. So, here I have gathered a few of the best hacking books of 2018 available on the market.

BEST HACKING BOOKS OF 2018

There are hundreds of books about hacking, but I have streamlined few of best hacking books of 2018.

1. THE HACKER'S PLAYBOOK PRACTICAL GUIDE TO PENETRATION

This handbook is about experting yourself with the hacking techniques in the hacker's way. This is about penetration testing that how hackers play their techniques and how we can counter them.

CONTENTS

  • Introduction
  • Pregame – The Setup
  • Setting Up a Penetration Testing Box
  • Before the Snap – Scanning the Network
  • The Drive – Exploiting Scanner Findings
  • The Throw – Manual Web Application Findings
  • The Lateral Pass – Moving Through the Network
  • The Screen – Social Engineering
  • The Onside Kick – Attacks that Require Physical Access
  • The Quarterback Sneak – Evading AV
  • Special Teams – Cracking, Exploits, Tricks
  • Post Game Analysis – Reporting
Download the Hacker's Playbook Practical Guide to Penetration.

2. ANDROID HACKER'S HANDBOOK

The Android Hacker's Handbook is about how the android devices can be hacked. Authors chose to write this book because the field of mobile security research is so "sparsely charted" with disparate and conflicted information (in the form of resources and techniques).

CONTENTS

  • Chapter 1 Looking at the Ecosystem
  • Chapter 2 Android Security Design and Architecture
  • Chapter 3 Rooting Your Device
  • Chapter 4 Reviewing Application Security
  • Chapter 5 Understanding Android's Attack Surface
  • Chapter 6 Finding Vulnerabilities with Fuzz Testing
  • Chapter 7 Debugging and Analyzing Vulnerabilities
  • Chapter 8 Exploiting User Space Software
  • Chapter 9 Return Oriented Programming
  • Chapter 10 Hacking and Attacking the Kernel
  • Chapter 11 Attacking the Radio Interface Layer
  • Chapter 12 Exploit Mitigations
  • Chapter 13 Hardware Attacks
Download Android Hacker's Handbook.

3. PENETRATION TESTING: A HANDS-ON INTRODUCTION TO HACKING

This book is an effective practical guide to penetration testing tools and techniques. How to penetrate and hack into systems. This book covers beginner level to highly advanced penetration and hacking techniques.

CONTENTS

  • Chapter 1: Setting Up Your Virtual Lab
  • Chapter 2: Using Kali Linux
  • Chapter 3: Programming
  • Chapter 4: Using the Metasploit Framework
  • Chapter 5: Information Gathering
  • Chapter 6: Finding Vulnerabilities
  • Chapter 7: Capturing Traffic
  • Chapter 8: Exploitation
  • Chapter 9: Password Attacks
  • Chapter 10: Client-Side Exploitation
  • Chapter 11: Social Engineering
  • Chapter 12: Bypassing Antivirus Applications
  • Chapter 13: Post Exploitation
  • Chapter 14: Web Application Testing
  • Chapter 15: Wireless Attacks
  • Chapter 16: A Stack-Based Buffer Overflow in Linux
  • Chapter 17: A Stack-Based Buffer Overflow in Windows
  • Chapter 18: Structured Exception Handler Overwrites
  • Chapter 19: Fuzzing, Porting Exploits, and Metasploit Modules
  • Chapter 20: Using the Smartphone Pentesting Framework
Download Penetration Testing: A Hands-On Introduction To Hacking.

4. THE SHELLCODER'S HANDBOOK

This book is about learning shellcode's of the OS and how OS can be exploited. This book is all about discovering and exploiting security holes in devices to take over.
Authors: Chris Anley, John Heasman, Felix "FX" Linder, Gerardo Richarte.

CONTENTS

  • Stack Overflows
  • Shellcode
  • Introduction to Format String Bugs
  • Windows Shellcode
  • Windows Overflows
  • Overcoming Filters
  • Introduction to Solaris Exploitation
  • OS X Shellcode
  • Cisco IOS Exploitation
  • Protection Mechanisms
  • Establishing a Working Environment
  • Fault Injection
  • The Art of Fuzzing
  • Beyond Recognition: A Real Vulnerability versus a Bug
  • Instrumented Investigation: A Manual Approach
  • Tracing for Vulnerabilities
  • Binary Auditing: Hacking Closed Source Software
  • Alternative Payload Strategies
  • Writing Exploits that Work in the Wild
  • Attacking Database Software
  • Unix Kernel Overflows
  • Exploiting Unix Kernel Vulnerabilities
  • Hacking the Windows Kernel
Download The ShellCoder's HandBook.

5. THE HACKER'S HANDBOOK WEB APPLICATION SECURITY FLAWS

This handbook is about finding and exploiting the web applications.
Authors: Dafydd Stuttard, Marcus Pinto.

CONTENTS

  • Chapter 1 Web Application (In)security
  • Chapter 2 Core Defense Mechanisms
  • Chapter 3 Web Application Technologies
  • Chapter 4 Mapping the Application
  • Chapter 5 Bypassing Client-Side Controls
  • Chapter 6 Attacking Authentication
  • Chapter 7 Attacking Session Management
  • Chapter 8 Attacking Access Controls
  • Chapter 9 Attacking Data Stores
  • Chapter 10 Attacking Back-End Components
  • Chapter 11 Attacking Application Logic
  • Chapter 12 Attacking Users: Cross-Site Scripting
  • Chapter 13 Attacking Users: Other Techniques
  • Chapter 14 Automating Customized Attacks
  • Chapter 15 Exploiting Information Disclosure
  • Chapter 16 Attacking Native Compiled Applications
  • Chapter 17 Attacking Application Architecture
  • Chapter 18 Attacking the Application Server
  • Chapter 19 Finding Vulnerabilities in Source Code
  • Chapter 20 A Web Application Hacker's Toolkit
  • Chapter 21 A Web Application Hacker's Methodology
So, these are the top 5 best hacking books on the market. There may be more fascinating books in the future that make take place in the top list. But for now, these are the best hacking books. Read and share your experience with these books.

Continue reading


  1. Paginas De Hackers
  2. Hacking 101
  3. Hacking Programs
  4. Hacking Microsoft

Masad Clipper And Stealer - Windows Spyware Exfiltrating Data Via Telegram (Samples)


Reference


"Masad Clipper and Stealer" steals browser information, computer files,  and automatically replaces cryptocurrency wallets from the clipboard with its own.
It is written using Autoit scripts and then compiled into a Windows executable.
It uses Telegram to exfiltrate stolen information.


Download

             Other malware


Hashes

SHA256SHA1MD5
1acf5a461ee16336eb8bbf8d29982c7e26d5e11827c58ca01adac671a28b52ad6001b34c17c122d201613fffd846b056614b66dae03234c2259c474aeb69500423ddeed7
290a1b89517dec10bfd9938a0e86ae8c53b0c78ed7c60dc99e4f8e5837f4f24a32800c10588053813f55bf8c87771311c5f7f38e2df4c1cf093c8373a8f2f194e77b69a2
7937a1068f130a90b44781eea3351ba8a2776d0fede9699ba8b32f3198de045ba2a67b06344e4f1cf85086f6b584316ec53d5e548368f1c4d8f0d908f5f4ff671df5f1da
87e44bca3cc360c64cc7449ec1dc26b7d1708441d471bf3d36cd330db35762942fe5483e6b82220eeeef12e531eb3347fea16ac11082ce517dd23eee335bedfc6bcd8205
cf97d52551a96dacb089ac41463d21cab2b004ba8c38ffc6cb5fb0958ddd34db5b79a15cb61f5260f0b9d807faa160e6d49590e4b5fdf9653eb1ffbdae8cb4f1f2d71747
79aa23c5a25c7cdbaba9c6c655c918dac3d9823ac62ebed9d7d3e94e1eaafc074a279a6b82fe801d3c8be9d16df2ef5623b177040029ab0fd56cd7e493b46a331ef18bd3
03d703f6d341be258ac3d95961ff0a67d4bf792f9e896530e193b091dca29c2ea9740352af2c9cc926deba7dffc452f213f7f05fa462aac76def5b53351b3b1ddb41124c
a368b6755e62e5c0ff79ea1e3bd146ee8a349af309b4acf0558a9c667e78293ae16167ab646381c277c2ca84319ceb57bacb2c92c4cdc7665adb1cda5897d4df4a560f88
ba933cefbe9a8034f0ba34e7d18481a7db7451c8ef4b6172fb0cad6db0513a5100749407e97085af470c75ef004f2235d30af44fc26a3f2317507a09d91014469b045384
3ba3c528d11d1df62a969a282e9e54534fb3845962672ad6d8bbc29cb6d062f5b8100890c0f1894544b3f99168377ec46c38e9114a0607b4488cd539b8b0b443abd121e3
b763054180cd4e24c0a78b49055ad36dbc849f1a096cddf2db8cee0b9338c21d7bec99308ce4bf409417b642cd9432000a5c19d22dfb1d606e5539399aa1a536baafd2f8
d5ce4b04b7eec6530a4a9d40510177468fadc235253e5a74530a8c9d990f3c5027fc204ffa42262b7570b6fccb435d4d38a3610fc5d8b73da810646407c333fe52186281
965a5949d8f94e17ebcd4cb6d0a7c19f49facbfc1b1c74111e5ceb83550d6c8f7698584b2e7c62061447a6a2583ed6957180c205e7ebe4411664672359b393f530fc2fc1
44134b9d4b10d94f6381b446a1728b116d62e65c1a52db45235af12caf7e38c0fd114077927d501606575ba9ab38ecfb3407d432a4388980d7e3539d74a950dab23d00ac
848d76a227f4fe282b7ddfd82a6dfc4c25da2735a684462b42fe4e1c413d8e34135cee7610890497183eb6251efef307ea013fe17bb23077b4f80df48b91b425eda05828
5ca0a957fe6c253827f344da4ba8692d77a4e21a1df4251594be2d27d87dd8aed231874332ca462fb462e4f68450d2c2c22d4bcddda77b3f3f74a2bdffd167917686e139
016fa511f6546ed439d2606c6db8821685a99f5a14ef3f710668b58dc89c69265c83749c62ee0131710bf26931cb1e463a8fbda3b0c34df85677d8f752dc1e1a5eeba0c9
22be594fbfa878f631c0632f6c4d260b00918817ff66a1f9f15efe44c1a58460856d635fca52631305f1fefc58eafa74496524b660ebf41953d5c6e212fc306cdb0c6519
f3571ec66288405dab43332ca03812617f85fb08832fbbe1f1d89901fe034b8a819485e20d841195e2e8a7ae5b41ff709887bb216984d37863c08b9fdd969297d35d3538
04c949eca23103b1de05278b49f42c3ab6b06f4bf20aafa5f2faefaa84c16ecd0487db2df1802dd4ee4ae3b62b5f08937dd5c77c4366ee61cbd7e636aea8540836a60036
d6fc04acda8f33a6d35eb577c27754c2f2b4d6f4869576c7c4e11b2c5e9b017683ae89826114662dad8553d5eeed5217b57047f22bc964e294d7ab314c34e5934d91a5a9
18c0bd4dd98008383fc52045ad896449fa7f0037593bb730ed1ef88aa547006dbcaa05b60a9d625852ac4f2d0d805ab16498815535d9f08c39c4cf396427f3a345e5c09a
4c9d5469e9095813418260045c2b11e499e4eaa0ffb25293f90f580c464157df4c6aacc0b893ed366f9f307326e59efa61e5153450dddaf7e5bb24aabf66eecd0c8b79cf
0b5f1fbc05dc8baca492b748adeb01fb4904e02723b59211ecde222f7b12d91e87f898e0d41c0f2c22d4e9278a942326877fc368da780b72140535d4c2d391e76dc8181d
31ad5c4547ceae4d0550c8460524c16a6105afc056760e872c4966656256c9dc37f485d3fa8f6cf13061cb1ea38ae0d5d2edfd95134aefcf640c24a1ab5344a96150fb05
edb00a0e5ff70e899857549e3263c887a799416c8bbab43ab130ca1be9bbd78c42c30dc551a3cb3bc935c0eae79b79f17942e439c2722241f765d2ad4fb58edd76a4adea
96f852b81760a425befaa11ea37c0cdea2622630bf2a0c94bb95042211ab614d5d9782064bc38d40c88f32c0410479cbd61caa40f332cfcda8c0ef579ede59eff23caa1e
57fd171a5b1a88e9583b42439851a91a940eb31105ab29cb314846da2ed43b820bfec2059823b936d782bea7bc16abd9923dddb56fff82df7a565b4570d299486697310f
277018b2cc6226dca6c7678cac6718c8584f7231340ad8cd7c03477559fdf48b261f916ce97ffc6817a4772705df68e6ccca8181009dc7d8766a85d85bb6a26ee69b66fe
e968affb1fc7756deb0e29807a06681d09a0425990be76b31816795875469e3dcf78484a999183324da9affdf2aaeff508d1dc473e1b8f6313447b8a4b49671ddeb8a4ee
4b1ccf6b823ee82e400ba25b1f532cd369d7e536475a470e2011b77ffeaf7bb3bc988f7cd32d411f2a9888afc72c7a892e2a1def55128a3da6f70129acdbf9dbe955cfe7
fc84d6636a34ad1a11dbaa1daec179e426bdcd9887b3d26dc06b202417c08f951df31bec02e35c9a4656bb3a3bdf631bb37605a855d77ab16377a8a314982f723fcc6fae
9ca15f15fbae58cb97b0d48a0248461e78e34e6d530338e3e5b91f209a1662678505dfaad6d10b84c73544eb748d547cb5bad9bdebc12c530dab0a65c37ffd72612fa705
31f3a402c1662ed6adffbf2b1b65cf902d1df763698eb76d21e4e94b4c62971418c972722d984ff6da2bc26a0aca4c7f209cc39c05bbf6e72b5b24c0c81e0671bf17b1e7
8d9f124ddd69c257189f1e814bb9e3731c00926fc2371e6ebe2654f3950ca02e553cd98c83e945ee3013aa40897baec0305b34a2b4030025e039c54c2d3923057447494c
a0923d7645604faaa864a079adeb741a5d6e65507a2819b2fee4835d396077d9f8e6995e28c789d8b24e982ac53d5d6ba453de73b796f85c8a7de71407d6e3c4206edda3
a19b790ea12f785256510dde367d3313b5267536a58ca0c27dbdac7c693f57e1a92f7393daf7ead9a44b12e35f850705798fc879a6defec886d31f6375712466dd794a96
f030fb4e859ee6a97c50c973a73dced3640befe37f579cfd15367ce6a9bbede2ad3a1e779f02539ccd07bff735e0823add9730b2c259564a8fe72333604a5686e30f6242
f01db6d77ac21211992ceae4e66e1e03c1cb39d61e03645b9369f28252ca769314c6bf63ff4d32d8a0a42e81ea39304fb7ab13c880fe593ef5538fbf66b3b3e1cb7b9b8b
dfe3d0e95feaed685a784aed14d087b019ba2eb0274947a840d2bdbae4ae36742107d057478328df8f538102508de00b0c4b37c7b5a85a0e7a2c4197c3794c8bb2eb5763
bf6083040ca51e83415f27c9412d9e3d700bd0841493b207bc96abf944ab0ca709a695ce6c35c029dd7577e29f403d7144698b417a2edceb31a9c0d05e5f13c6caee0576
b154151dc8ace5c57f109e6bb211a019db20c4f0127c4d13c7703f730bf492768c0cda049c85493df4e97db3db4ddc94075ba62cb6a895ac5ba5b6472680d47410a238a5
6bf6b1bde63cee9b81902efd187fdd56ecee5853754ce0a19d5ab5c3b02429886e2d4f0bcc97ce130ae89647f648d3e96548a391a29f9d176b913e7f693355700aaadbb9
0dcf547bd8f4074af97416d8b84ea64b2f3319064aa4bce64ad0c2e2d3957175a996b925e9391a69140caf6e4adba928694ffe66dd575413a40839f2807593aa21c71152
6cff1249cc45b61ce8d28d87f8edc6616447e38168e610bed142f0b9c46ea6849baa823deb9075e8df77b891115c019244de09de488bb5c0739485721182c01a82b01d14
5b5ebe019806885bbaafe37bc10ca09549e41c240b793fd29a70690a5d80b4963d46711f9064b96ff2d0affdef1ecd82d120659db95e2d8a8509ac05f5445d18d32cc7cb
103d87098c9702cab7454b52869aeeb6a22919f29a7f19be7509255ce2d8c83ee29a163488438c9ea9014ddf1a9b2d382cc5d7e6baf2587fafaedbab4a78b9b7fd8b55f8
c73675005a09008bc91d6bc3b5ad59a630ab4670dca6ac0d926165a3ecfd8d92d8ea2280cd06a5cc32b7d668e2b4b2e68f3a7e2a98ecc6fbb2cb5649daf751fcbfb81bcb
ef623aadd50330342dc464a31b843b3d8b5767d62a62f5e515ac2b380b208fbe620ff5a7aaf7f3fcf4abc9365e0e77b3ec4b434db14535c5835c9dfb3cbbc7f6fef6034c
More articles

How To Start | How To Become An Ethical Hacker

Are you tired of reading endless news stories about ethical hacking and not really knowing what that means? Let's change that!
This Post is for the people that:

  • Have No Experience With Cybersecurity (Ethical Hacking)
  • Have Limited Experience.
  • Those That Just Can't Get A Break


OK, let's dive into the post and suggest some ways that you can get ahead in Cybersecurity.
I receive many messages on how to become a hacker. "I'm a beginner in hacking, how should I start?" or "I want to be able to hack my friend's Facebook account" are some of the more frequent queries. Hacking is a skill. And you must remember that if you want to learn hacking solely for the fun of hacking into your friend's Facebook account or email, things will not work out for you. You should decide to learn hacking because of your fascination for technology and your desire to be an expert in computer systems. Its time to change the color of your hat 😀

 I've had my good share of Hats. Black, white or sometimes a blackish shade of grey. The darker it gets, the more fun you have.

If you have no experience don't worry. We ALL had to start somewhere, and we ALL needed help to get where we are today. No one is an island and no one is born with all the necessary skills. Period.OK, so you have zero experience and limited skills…my advice in this instance is that you teach yourself some absolute fundamentals.
Let's get this party started.
  •  What is hacking?
Hacking is identifying weakness and vulnerabilities of some system and gaining access with it.
Hacker gets unauthorized access by targeting system while ethical hacker have an official permission in a lawful and legitimate manner to assess the security posture of a target system(s)

 There's some types of hackers, a bit of "terminology".
White hat — ethical hacker.
Black hat — classical hacker, get unauthorized access.
Grey hat — person who gets unauthorized access but reveals the weaknesses to the company.
Script kiddie — person with no technical skills just used pre-made tools.
Hacktivist — person who hacks for some idea and leaves some messages. For example strike against copyright.
  •  Skills required to become ethical hacker.
  1. Curosity anf exploration
  2. Operating System
  3. Fundamentals of Networking
*Note this sites


More articles


  1. Hacking Iphone
  2. Hacking Smart Tv
  3. Tutoriales Hacking
  4. Kali Hacking
  5. Nfc Hacking
  6. Funnel Hacking Live
  7. Hacking-Lab

Top 15 Best Operating System Professional Hackers Use

Top 10 Best Operating System Professional Hackers Use

Top 15 Best Operating System Professional Hackers Use

Top 15 Best Operating System Professional Hackers Use

A hacker is someone who seeks and exploits the weaknesses of a computer system or network computing. Hackers may be motivated by a multitude of reasons, such as profit, protest, challenge, enjoyment or to assess these weaknesses to help in removing them.
The listed operating systems are based on the Linux kernel so it is all free operating systems.

1. Kali Linux

Kali Linux maintained and funded by Offensive Security Ltd. and it is first on our list. Kali Linux is a Debian-derived Linux distribution designed for digital forensics and penetration testing. It was developed by Mati Aharoni and Devon Kearns of Offensive Security through rewriting BackTrack, its previous forensics Linux distribution based on Ubuntu. Kali Linux has a specific project for the withdrawal of compatibility and portability of Android-specific devices, called Kali Linux NetHunter. It is the first open test platform penetration Source for Nexus Android devices, created as a joint effort between the member of the Kali "BinkyBear" Security and offensive community. It supports Wireless 802.11 frame injection, one-click configurations MANA Evil access point, keyboard HID (Teensy as attacks), as well as attacks MITM USB Mala.

2. Back Box

Back Box is an evaluation penetration testing Linux distribution and Ubuntu-based security aimed at providing an analysis of computer network systems and toolkit. Desktop environment back box includes a complete set of tools needed for ethical hacking and security testing.

3. Parrot Security OS

Parrot Security OS is a GNU / Linux distribution based on Debian. Fue built in order to perform penetration tests (safety information), vulnerability assessment and mitigation, Computer Forensics and Anonymous Surfing. Ha been developed by the team of Frozen box.
Parrot is based on the stable branch (Jessie) of Debian, a Linux 4.1 kernel hardened customized with a branch grsecurity patched available. The desktop environment is MATE fork of Gnome 2, and the default display manager is LightDM. The project is certified to run on machines with 265MB of RAM minimum follow and it is suitable for both 32-bit (i386) and 64-bit (amd64), with a special edition that works on 32-bit machines of age (486). Moreover, the project is available for Armel and armhf architectures. It even offers an edition (both 32 bit and 64 bit) developed for servers only for pen testing cloud.

4. Live Hacking OS

Live Hacking OS is a Linux distribution packed with tools and utilities for ethical hacking, penetration testing, and countermeasure verification. It includes embedded GUI GNOME user. There is a second variation available which has only the command line and requires much fewer hardware requirements.

5. DEFT Linux

DEFT stands for Digital Evidence and Forensic Toolkit and it is a distribution of Linux open source software built around the DART (Toolkit for Advanced Response Digital) and is based on the Ubuntu operating system. It has been designed from scratch to offer some of the best computer forensics open source and incident response tools that can be used by individuals, IT auditors, investigators, military, and police.

6. Samurai Web Testing Framework

The Samurai Web Testing Framework is a live Linux environment which has been pre-configured to function as a web pen-testing environment. The CD contains the best of open source and free tools that focus on testing and websites that attack. In the development of this environment, it is based on our selection of tools that we use in our practice of security. Hence, it includes the tools that were used in the four steps of a pen-test web.

7. Network Security Toolkit

The Network Security Toolkit (NST) is a Live CD based on Linux that provides a set of security tools computing and open source network to carry out routine security tasks and diagnostic networks and tracing. The distribution can be used as an analysis of network security, validation and monitoring tool for servers hosting virtual machines. NST has management capabilities similar to Fedora packages and maintains its own repository of additional packages.

8. Bugtraq

Bugtraq is a mailing list dedicated to safety issues in computers. On-topic issues new discussions about vulnerabilities, security-related notices providers, operating methods, and how to fix them. This is a mailing list of large volume, and almost all new vulnerabilities are there. Bugtraq computer freaks and experienced developers are discussed, is available in Debian, Ubuntu and openSUSE 32 and 64-bit architectures.

9. NodeZero

NodeZero is an open source system based on the operating core derived from the most popular Linux distribution in the world, Ubuntu, and designed to be used for penetration testing operations. The distribution can be downloaded as an ISO image live DVD, which will also take place on computers that support both 32-bit (x86) and 64-bit (x86_64) instruction set. Besides the fact that it allows you to start the live system, start menu contains several advanced features such as the ability to perform a diagnostic test of system memory, boot from local disk options, start the installer directly and to start in safe graphics mode, text mode or in debug mode.
Default graphical desktop environment NodeZero is powered by GNOME, which uses the classic GNOME interface. It has a design of two panels and uses the default software repositories of Ubuntu.

10. Pentoo

Pentoo is a Live CD and Live USB OS designed for penetration testing and security assessment. It is based on Gentoo Linux, Pentoo is offered both as 32-bit and 64-bit live cd which is installable. Pentoo is also available as a superposition of an existing Gentoo installation. It has conductors packet injection patched wifi, GPGPU cracking software, and plenty of tools for penetration testing and security assessment. The kernel includes Pentoo grsecurity and PAX hardening and additional patches with the binary compiled from a string of hardened with the latest nightly versions of some tools that are available.

#11 Live Hacking OS

Well, this Linux distro actually comes with some useful hacking tools which are often used in penetration testing or ethical hacking purpose. Live Hacking OS consists of the GNOME inbuilt. The operating system is really easy to operate and it can work on less RAM.

#12 Knoppix STD

This is another best Linux distro which focuses on tools for computer security. Knoppix STD brings some advanced tools for Password cracking, Firewalls, Network Utilities, Honeypots, Wireless Networking and more. This is one of the most used operating systems for Hackers.

#13 Cyborg Hawk

Cyborg Hawk is a new operating system which is based on Ubuntu Linux. Well, lots of hackers talk about Cyborg hawk and its one of the most powerful and cutting-edge penetration testing distribution that has ever been created. The operating system houses more than 700 tools for different purposes.

#14 Blackbuntu

Well, this is another operating system which is based on Linux and it was specially developed for penetration testing. Well, the operating system is very famous amongst hackers and it offers an awesome platform to learn Information security.

#15 Weakerth4n

Well, this is another best operating system which is used by professional hackers. WeakerTh4n actually comes with lots of hacking tools and it's actually a modern operating system for WiFi Hacking. Some of the wireless tools include SQL Hacking, Password Cracking, WiFi attacks, Cisco exploitation and more.
Continue reading